Digital identity is unusual among technology topics because its failures fall hardest on people who already have the least power to object. Prove who you are and you can open an account, claim a benefit, see a doctor. Fail to prove it, and you can be locked out of services you are legally entitled to. The World Bank’s ID4D initiative describes trusted identity as a route to wider access while warning that people without documents, connectivity or an accessible enrolment route can be left behind. Both halves of that sentence are the point.
The access case
For someone with no formal papers, a recognised identity can be transformative. It is the key that unlocks a bank account, a SIM card, a school place, a pension. The World Bank estimates that roughly 850 million people still lack a legal form of identification, a large share of them in Sub-Saharan Africa. Closing that gap is a genuine public good, and digital tools can make enrolment faster and verification cheaper where the alternative is a slow paper process.
The risk case
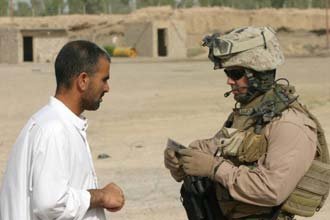
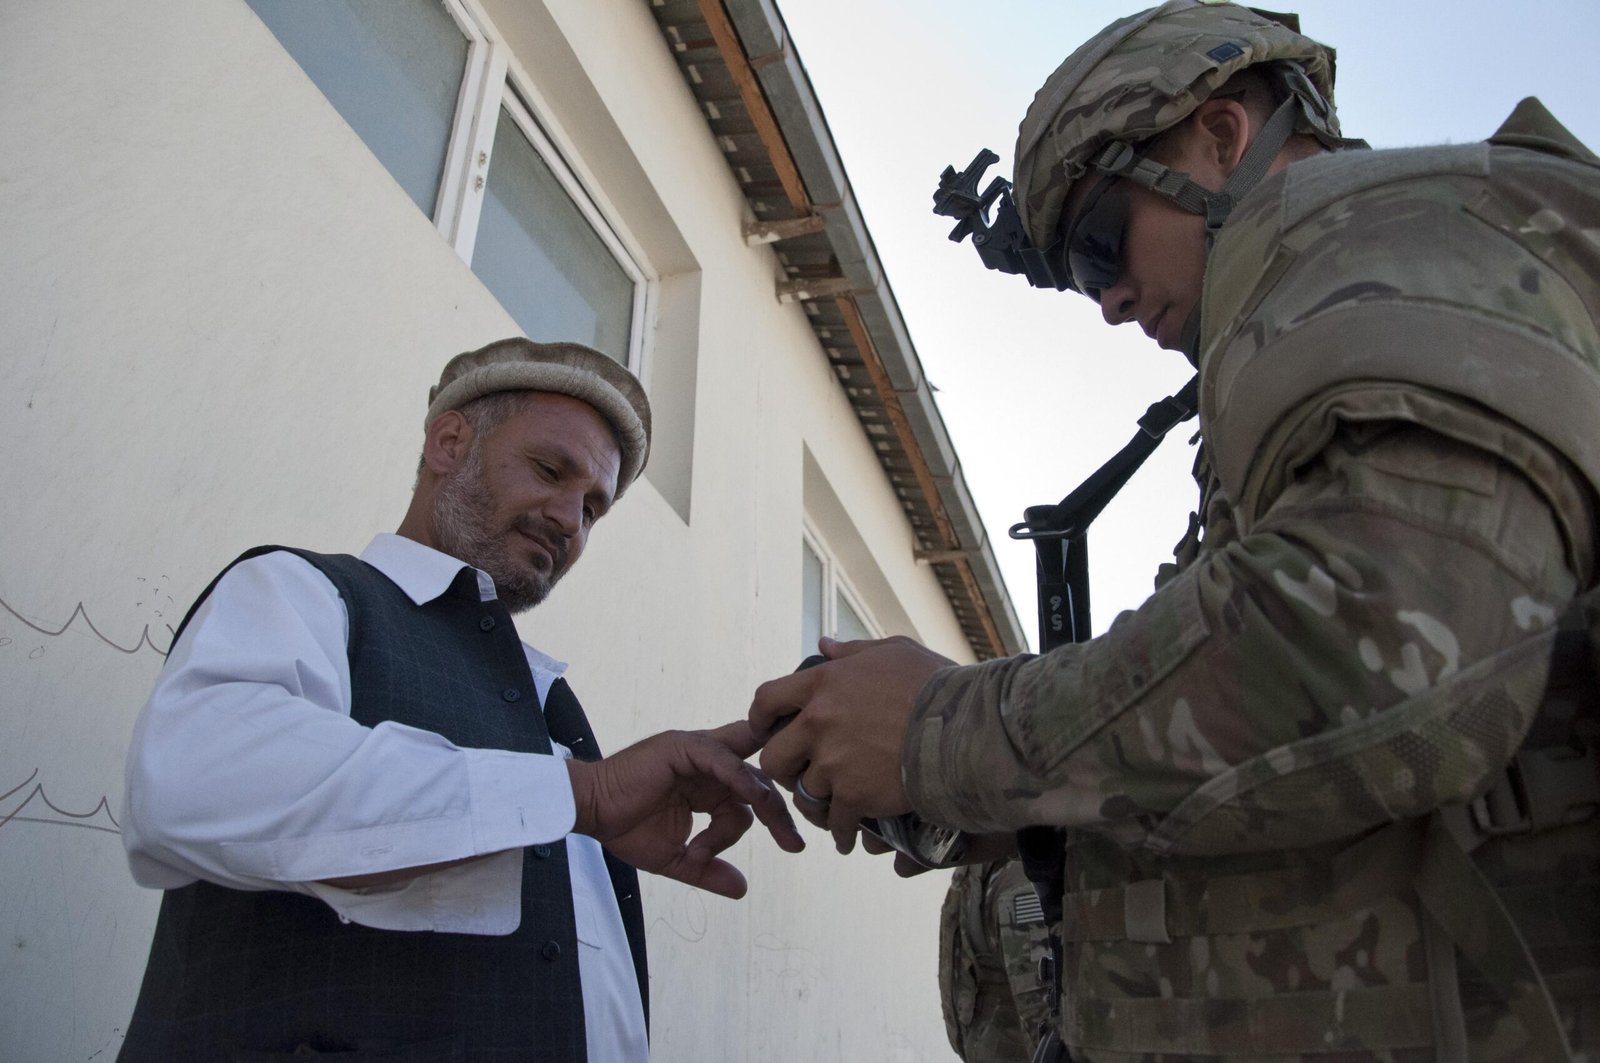
The same system that widens access can narrow it. A biometric check that fails for a manual labourer with worn fingerprints excludes that person. A database that centralises many services creates a single point of failure and a single attractive target. Rules that make identity mandatory for everyday life can turn a technical error into a loss of food, income or medicine. These are not hypothetical: exclusion at authentication and concerns over data governance recur in coverage of large identity programmes.
Four safeguards that change the outcome
Enrolment that meets people where they are. Mobile registration, flexible documents and assisted channels matter more than elegant apps. If enrolment assumes a fixed address and a smartphone, it will miss the people it is meant to reach.
A real route to correct errors. Anyone can be mis-identified. The test is how quickly and cheaply that is fixed, and whether the process is accessible without a lawyer. A published service standard with a time limit is a reasonable minimum.
Data minimisation and visibility. The less a central system stores, the less a breach can expose. Logging every access and letting people see who looked at their record turns transparency from a slogan into a feature.
Limits on mandatory use. The more services that require the identity, the higher the cost of being excluded. Legal limits on secondary use and on compulsory linking protect people when something goes wrong.
It rarely arrives as a dramatic denial. More often it is a queue that closes before a shift worker arrives, a form that demands a document she never had, or a fingerprint reader that will not read a farmer’s hands. Designing for these cases determines whether the programme’s headline enrolment numbers translate into real access.
How to tell a good system
Ask who can enrol and who cannot. Ask what happens when authentication fails, and how a person appeals. Ask who can see the data and under what rules. Ask whether the system uses open standards or ties agencies to a single vendor. A system that answers these well can expand access without quietly creating a new kind of exclusion — and that is the only version of digital identity worth building.
The governance question
Most of the risk in digital identity is not technical. It is about who sets the rules, who can change them, and how those decisions are reviewed. A biometric database governed by a single ministry with no external oversight is a different proposition from one subject to independent audit and a data-protection authority. The technology is similar; the consequences are not. When evaluating a programme, the governance arrangements deserve as much attention as the enrolment numbers.
The lessons recur across very different systems. Peru’s identity agency, Estonia’s X-Road, India’s Aadhaar and the Philippines’ PhilSys each illustrate a version of the same tension between scale and protection. Where enrolment was made flexible, uptake among marginalised groups improved. Where appeals were slow, exclusion complaints grew. Where secondary use was left loosely defined, public trust fell. None of those outcomes was determined by the software; each followed from design and governance choices made early and changed only at cost.
A practical test
Before trusting a system with something as consequential as identity, ask whether a person can use it without a smartphone, whether they can fix an error within a stated time, and whether they can find out who accessed their data. If the answer to any of these is no, the programme is not yet ready to be a gatekeeper for essential services.
This report draws on the World Bank’s Identification for Development (ID4D) programme.
Image: Government of Transnistria · Public domain · via Wikimedia Commons.